AI readiness | Published August 6, 2026
The Permission Envelope: What an Operations AI May Read, Recommend, and Change
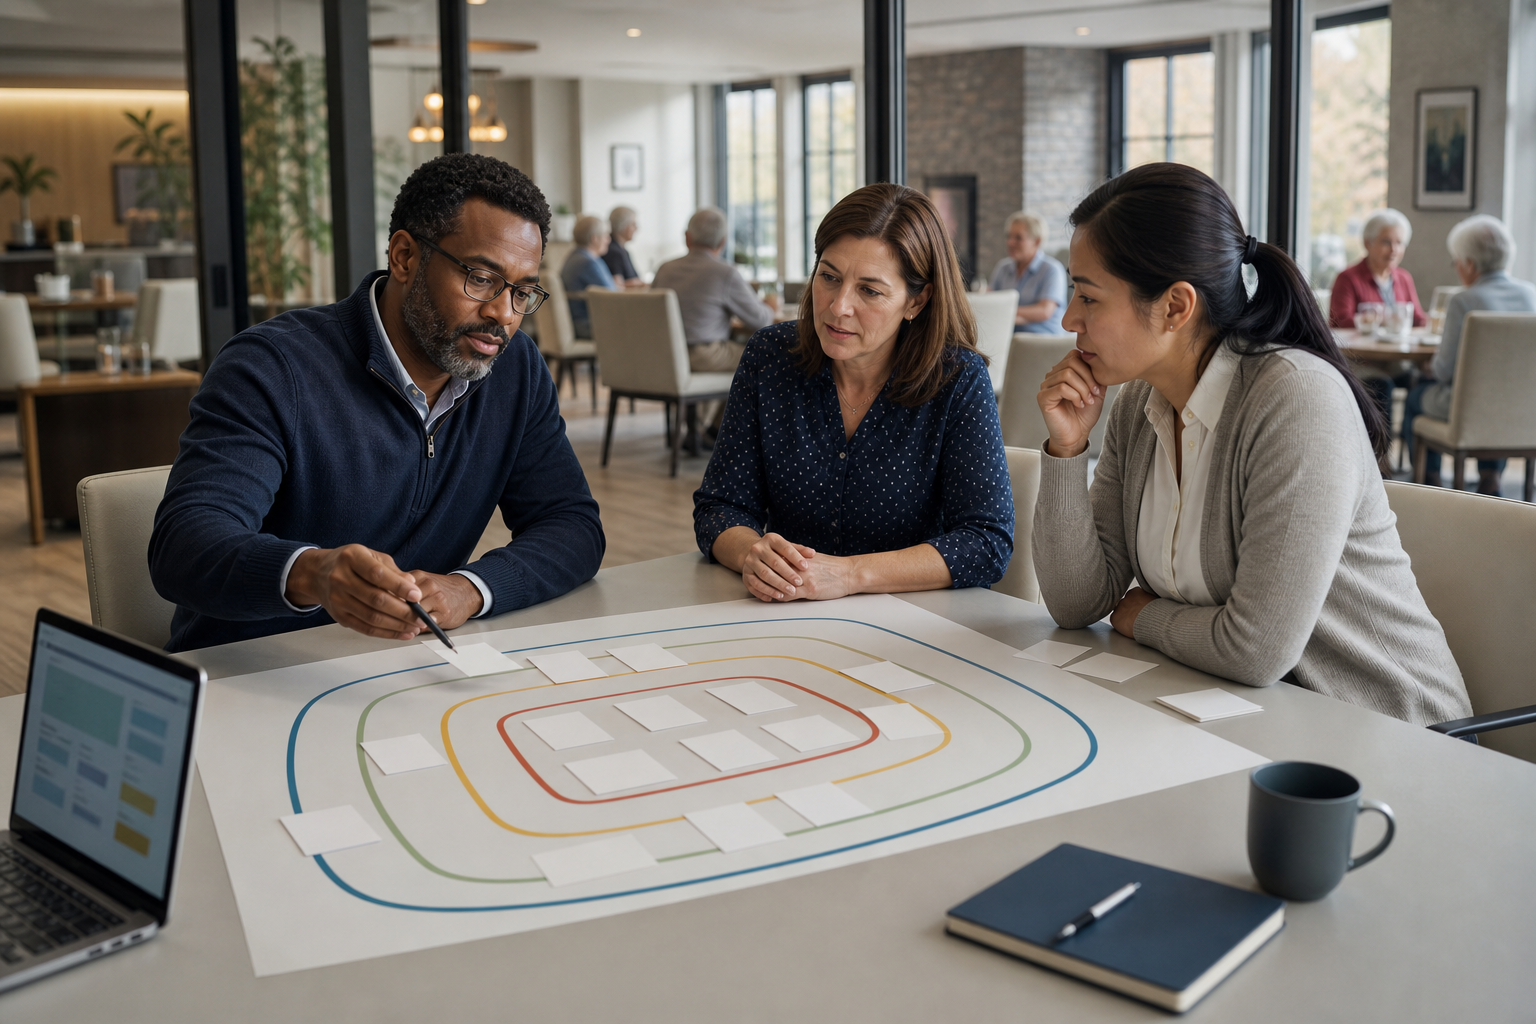
An assistant is not safe merely because its prompt says “ask before acting.” A deployable control must define the exact data, tools, actions, conditions, time window, and human owner that form its permission envelope.
NIST's July 22–23 AI security workshop addressed architecture, access control, storage, deployment, and agentic workflows. The NIST AI Agent Standards Initiative provides broader work on secure and interoperable agents. A July 15 UK government call for evidence underscores the operational importance of understanding how data is used and governed in AI-intensive systems.
Keep approved knowledge, workflow ownership, and system context connected through the ServingIntel Genesis platform.
Define four authority levels
- Read: retrieve only approved fields from approved sources.
- Recommend: produce a proposed decision with evidence and uncertainty.
- Prepare: create a reversible draft, ticket, message, or transaction for review.
- Change: execute a specifically allowed action within a tested boundary.
Grant each level separately. Permission to read a resident preference does not imply permission to change it. Permission to draft a menu update does not imply permission to publish it.
Write the envelope as a control record
- Name the business purpose and accountable owner.
- List allowed sources, fields, tools, and destinations.
- List prohibited data, actions, and combinations.
- Set value, volume, location, and time limits.
- Define evidence required before action.
- Define human review, stop, rollback, and incident routes.
Use ServingIntel solutions to connect an AI use case to the actual operating gap rather than beginning with a generic capability.
Test denied behavior deliberately
A permission test should prove what the assistant cannot do. Ask it to use an unapproved source, exceed a threshold, act outside the service window, modify a protected field, conceal missing evidence, and continue after a stop signal. The correct result is a clear refusal or escalation with a useful reason.
The POS University automation-readiness playbook offers a companion physical-workflow lens. Use the Support4POS outage playbook to test degraded-mode behavior.
Require evidence with every consequential recommendation
The assistant should identify the source, effective date, retrieval time, relevant record, uncertainty, and action owner. If the evidence is stale, incomplete, conflicting, or outside scope, the recommendation should stop. Review governance and accuracy developments through ServingIntel News & Insights.
Review permissions like production access
Revalidate permissions after a model, connector, role, source, destination, or workflow changes. Remove unused access, rotate credentials through the approved process, and preserve decision logs without exposing secrets. Route defects through ServingIntel support resources.
The bottom line: useful AI readiness is not a broad “yes” to automation. It is a narrow, testable permission envelope that makes safe behavior—and safe refusal—observable.